Financial documents are central to timely reporting and regulatory compliance, yet inconsistent filing and weak metadata create preventable risk. A deliberate approach to patterns — naming, metadata, storage hierarchy, and retention — reduces errors and accelerates access. Teams that standardize document practices shorten audit cycles and improve decision quality. This article outlines practical steps to make financial records more reliable and searchable. Adopting patterns need not be disruptive when rolled out with clear priorities.
Assessing Document Risk
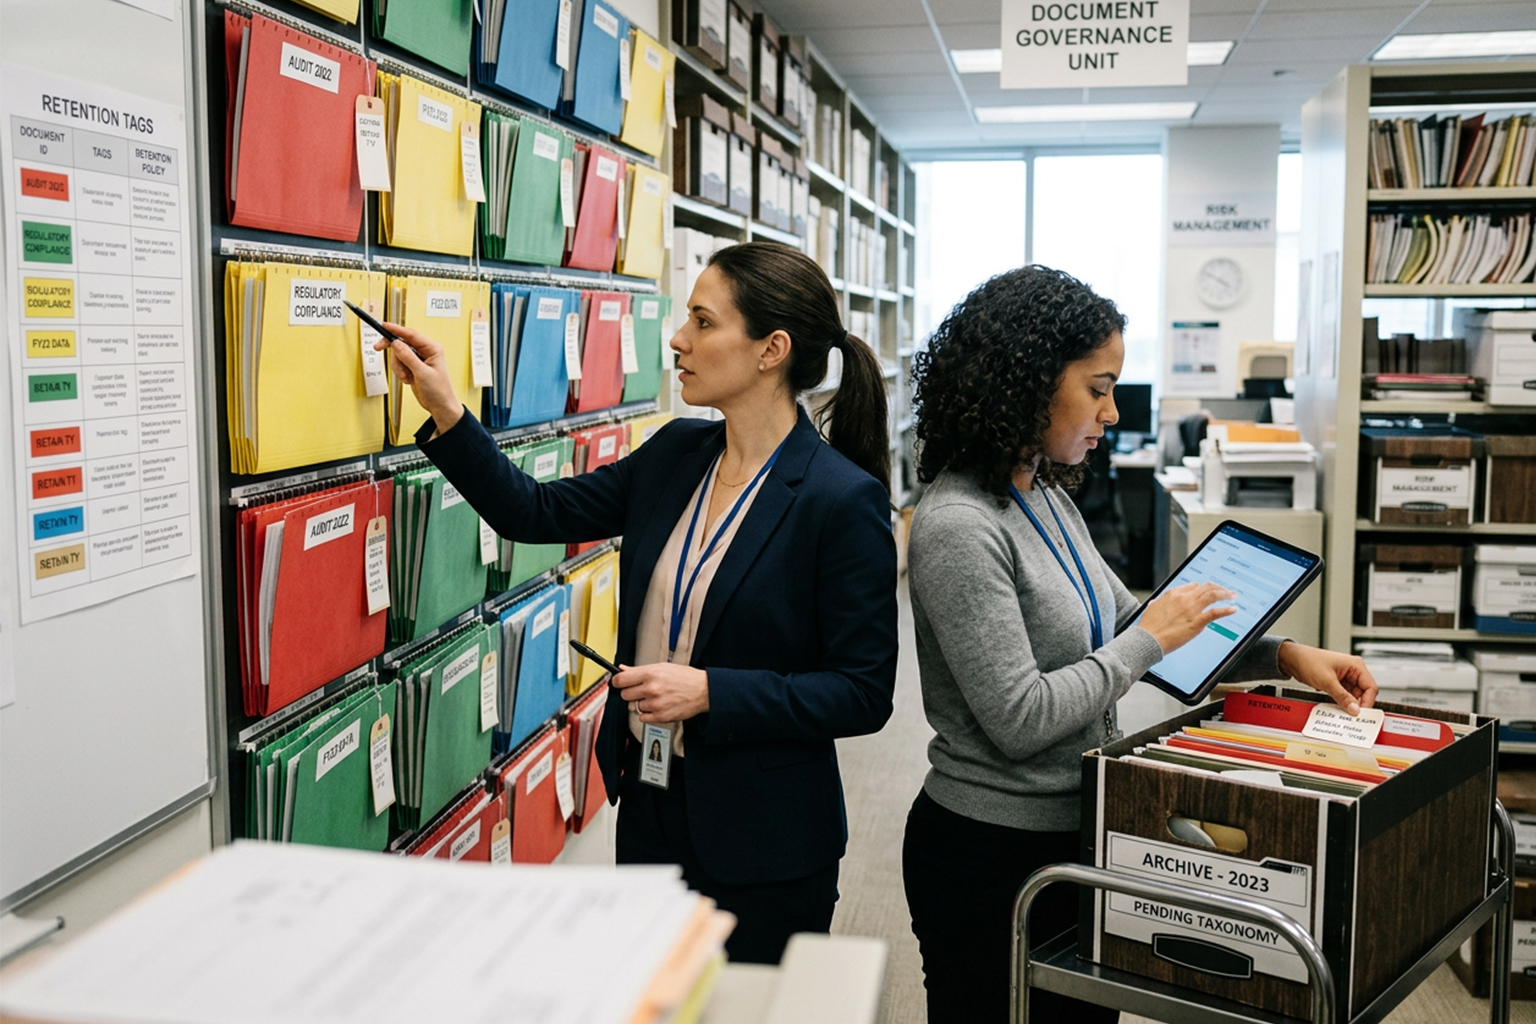
Begin by mapping the types of documents your organization generates and the risks associated with each class, such as audit exposure or data loss. Identify high-value records like ledgers, contracts, tax filings, and reconciliations, then assign retention and access priorities. Use simple taxonomies that mirror reporting workflows to avoid ambiguous categories that hinder retrieval. Regularly review the map to accommodate new instruments and regulatory changes. Where possible, estimate the time saved by improved retrieval to justify investment.
Clear risk assessment informs subsequent naming and storage rules. It also helps prioritize automation and archival decisions. Documenting decisions during reviews builds institutional memory.
Naming, Metadata, and Indexing
Consistent naming conventions and metadata are the backbone of searchable archives, enabling both people and tools to find the right files. Define a compact filename structure that includes date, entity, document type, and version flag, and pair it with metadata fields for period, department, and responsible owner. Implement controlled vocabularies and templates to reduce variability and support bulk tagging during ingestion. Embrace searchable metadata over long filenames when using modern repositories.
Good indexing reduces time spent locating files and improves reporting velocity. Training and quick reference guides help ensure adoption across teams.
Governance, Versioning, and Access
Governance should define roles, permissions, and versioning policies so only authorized changes propagate into official records. Maintain an immutable audit trail and a clear process for approvals, redactions, and release to external parties. Automate retention and disposition rules to prevent over-retention and to simplify compliance during audits. Use access controls and encryption to balance availability with the protection of sensitive financial information.
Combining technical controls with clear responsibilities prevents accidental data exposure. Regular drills and audits keep the governance model effective and current.
Conclusion
Smarter document patterns reduce operational risk and make financial reporting faster and more defensible. Start with a risk map, adopt consistent naming and metadata, and lock in governance and automation. Small, sustained improvements yield measurable benefits for teams and stakeholders.

