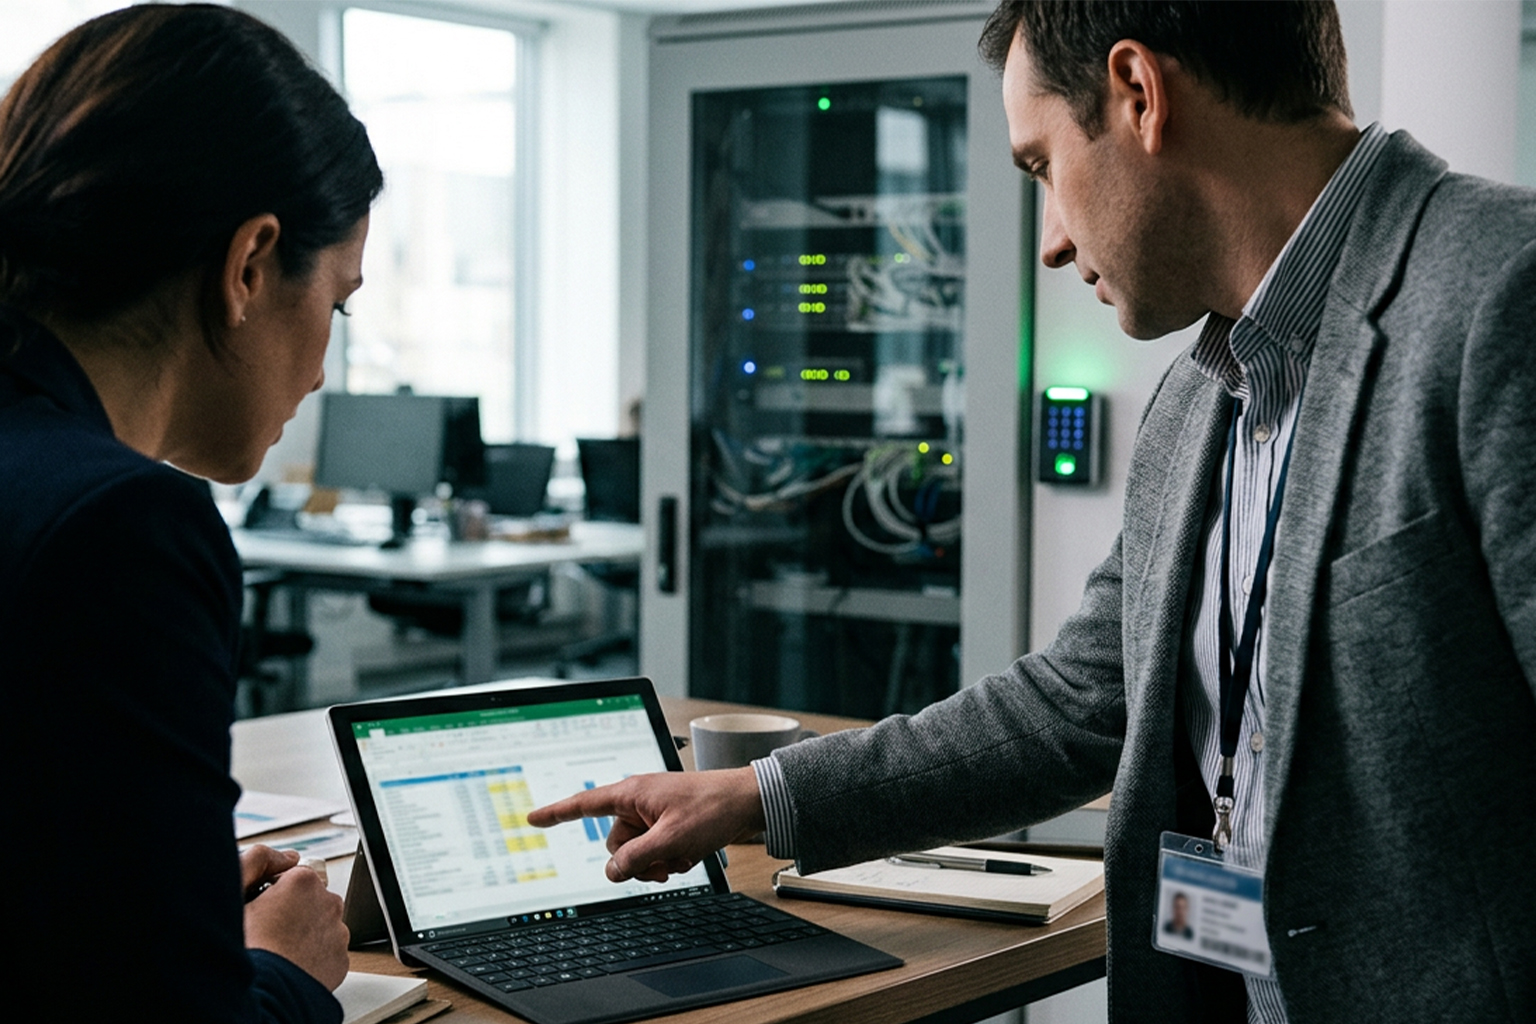
Financial document systems must reconcile two competing priorities: making records easy to access for authorized users while keeping sensitive information secure. Achieving this balance affects compliance, operational efficiency, and risk management across the organization. A considered approach reduces the chance of data breaches without slowing down routine financial workflows. This article outlines practical steps to align access and security in a finance-focused document environment.
Why accessibility and security both matter
Accessibility ensures finance teams can retrieve invoices, statements, and contracts quickly to support decision making, reporting, and audits. Security protects confidential data, prevents unauthorized disclosures, and helps maintain regulatory compliance. Neglecting accessibility leads to operational delays and duplicate work, while ignoring security invites regulatory penalties and reputational harm. Both dimensions are business-critical and must be designed together rather than treated as separate priorities.
Framing both needs as complementary goals helps teams prioritize controls that enable work rather than block it. When stakeholders understand trade-offs, they are more likely to support sensible policies.
Practical controls to hit the balance
Start with role-based access controls that grant permissions by job function rather than ad hoc user lists, which reduces over-permissioning. Combine that with document-level encryption, secure transmission protocols, and robust authentication, such as multi-factor authentication for privileged access. Implement audit logging and alerting so unusual access patterns can be investigated promptly. These measures protect sensitive records while allowing legitimate users the access they need.
- Define roles and least-privilege permissions.
- Use encryption at rest and in transit.
- Deploy logging, monitoring, and access reviews.
By standardizing these controls, organizations reduce manual exceptions and keep security predictable and manageable.
Policies, workflows, and user experience
Clear policies translate security requirements into everyday workflows that finance teams can follow without friction. Standard templates, metadata schemas, and intake processes speed document capture and classification while enforcing retention rules. Training and concise guidance help users understand why controls exist and how to comply efficiently. Streamlined workflows paired with policy help reduce risky workarounds and shadow storage.
Regular policy reviews ensure workflows adapt as teams and regulations change. Involving end users in design improves adoption and minimizes disruption.
Technology integration and automation
Choose systems that integrate with core finance tools, identity providers, and backup solutions to reduce manual handoffs and potential security gaps. Automation can enforce retention schedules, redact sensitive fields for broader access, and trigger approval workflows when exceptions arise. APIs and connectors make it easier to apply consistent controls across repositories and third-party services. Practical integrations reduce complexity and improve both security posture and user productivity.
Start with a small pilot to validate integrations before scaling, which minimizes risk and uncovers real-world needs.
Conclusion
Balancing accessibility and security in financial document systems requires deliberate controls, clear policies, and thoughtful technology choices. When designed together, these elements protect sensitive data while empowering finance teams to work effectively. Continuous review and user-centered design keep the balance aligned with evolving business needs.

