Managing financial documents requires clear policies that guide what to retain, how to secure, and when to dispose. A policy-driven lifecycle reduces ambiguity across teams and supports regulatory compliance. Establishing these rules early prevents ad hoc behaviors that create risk and inefficiency. This approach balances operational efficiency with compliance needs. This article outlines a practical approach to building and enforcing document lifecycle policies.
Defining lifecycle stages
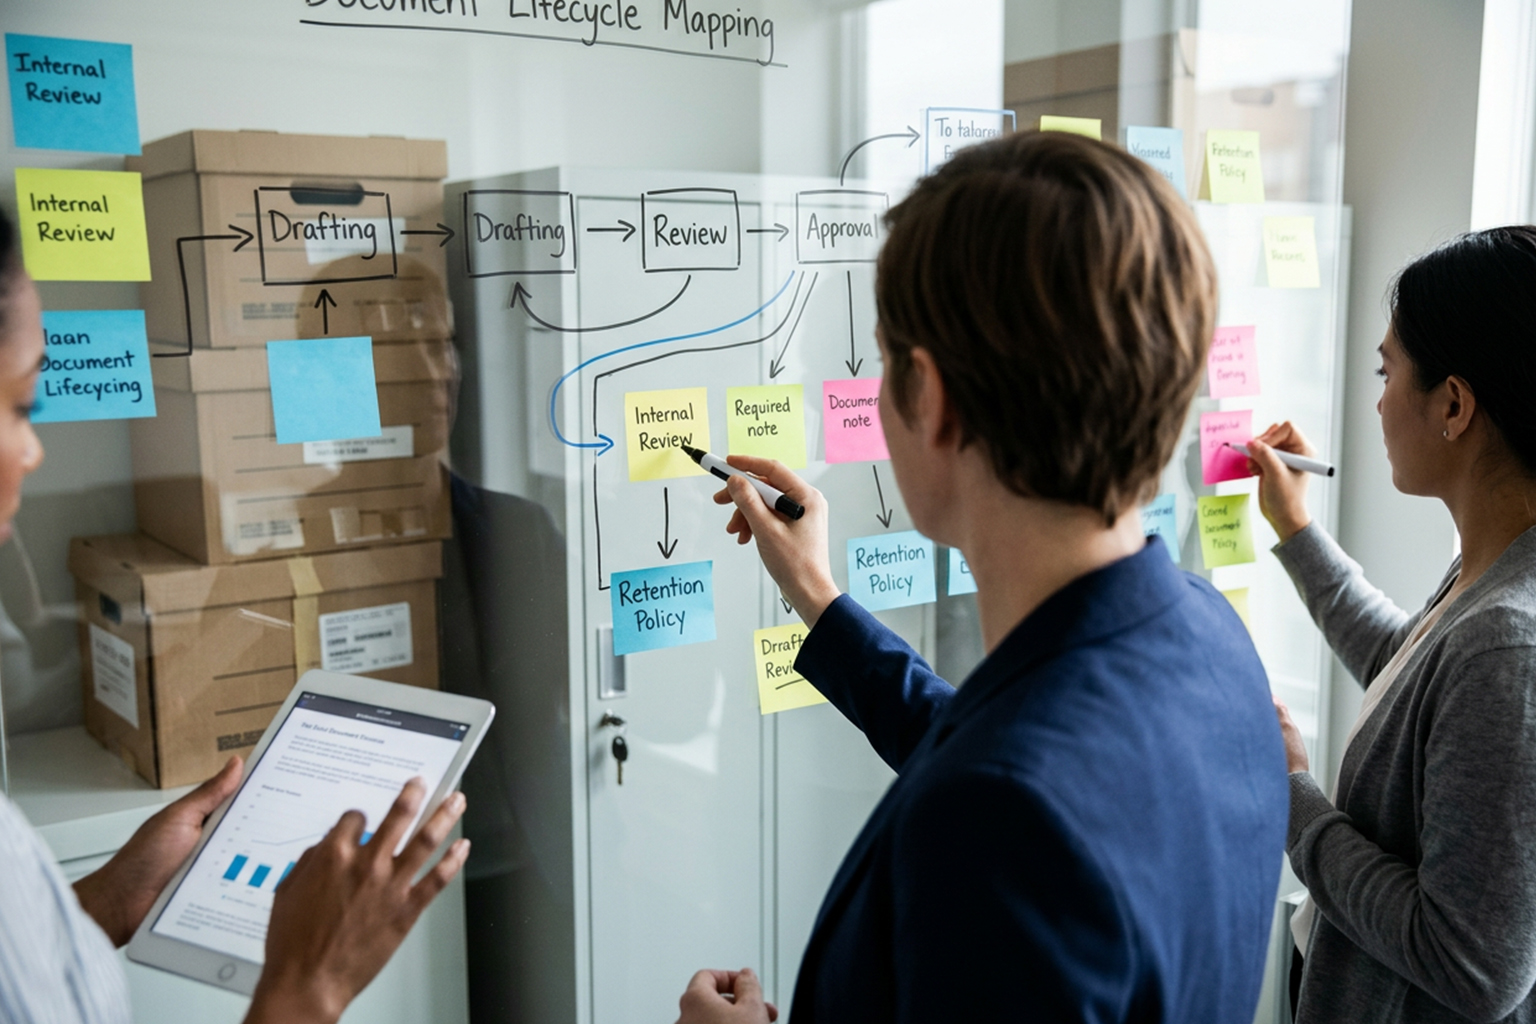
Begin by mapping document types and stages: creation, classification, active use, storage, archival, and disposal. Each stage should have defined responsibilities and triggers that move a document to the next state. Classify documents by sensitivity and retention drivers, such as legal requirements or business value. Clear stage definitions help automate actions and ensure consistent handling. Ensure stage definitions align with existing business workflows to minimize disruption.
Assigning owners for each stage creates accountability and speeds decision-making. This reduces delays and unclear handoffs during audits.
Policy elements and access controls
A robust policy specifies retention periods, access permissions, version control, and acceptable formats. Access controls should be least-privilege and tied to roles rather than individuals, with periodic reviews to adjust privileges. Versioning rules and audit trails preserve provenance and support dispute resolution. Encryption, watermarking, and controlled sharing reduce unauthorized exposure.
Combine technical controls with training so staff understand their responsibilities. Regular policy reviews ensure controls stay aligned with evolving risks.
Automation, retention, and audit readiness
Automation reduces manual errors by enforcing retention schedules and archival flows through rules and workflows. Tagging and metadata enable precise searches and bulk actions that align with retention policy triggers. Integrating with backup and legal hold processes prevents accidental deletion during litigation or audits. Monitoring and reporting tools surface exceptions and support timely remediation.
Start small with high-impact document sets and expand automation iteratively. Measured rollouts help catch edge cases before broad enforcement.
Implementation and governance
Successful rollout starts with a pilot that targets a few high-priority document sets and business units. Engage stakeholders from legal, compliance, finance, and IT to align retention, access, and legal-hold rules before automation. Define success metrics such as retrieval time, compliance exceptions, and reduction in storage costs to measure impact. Provide role-based training and clear escalation paths to address questions during transition. Use feedback loops to refine classifications, metadata schemas, and automation rules.
Establish a governance board to review policy changes and handle exceptions. Regular reporting on KPIs keeps leadership informed and drives continuous improvement.
Conclusion
A policy-driven lifecycle for financial documents strengthens governance and operational efficiency. By defining stages, controls, and automation, organizations reduce risk and improve accessibility. Regular review and clear ownership keep the system resilient as requirements change.

